

tag
#security
The technical heart: vulnerability research, disclosure, threat analysis, the craft of finding and fixing
9 Must-See Talks at #hackersummercamp 2022
Here's a list of the talks that I'm going to get myself along to at Blackhat and DEF CON this year, and why...
Digital and Personal Self-Care at #hackersummersamp — "New Normalish" Edition
I usually write a piece for first-timers and newbies on how to get the most out of Hacker Summer Camp and how to stay safe digitally and physically. This tradition began in the early days of Bugcrowd, when DEF CON was part of new-hire induction.
Two-thirds of ethical hackers considering bug bounty hunting as a full-time career
Casey Ellis, founder and CTO at Bugcrowd, said bug bounty hunters are ultimately entrepreneurs in their own right.
[TRANSCRIPT] Threats that may have gone unnoticed by organizations during the pandemic
Casey Ellis, the founder, chairman and CTO of Bugcrowd, told SC Media Senior Reporter Joe Uchill that companies should think about the various threat scenarios that emerged over the last year that they may have missed as employees return to the office environment.
[TRANSCRIPT] Threat hunting in the age of work-from-home
Casey Ellis, the founder, chairman and CTO of Bugcrowd, told SC Media Senior Reporter Joe Uchill that there’s always going to be corporate infrastructure that provides information for a threat hunter, such as VPN, antivirus, and endpoint detection and response.
IT Visionaries Podcast with Malcolm Harkness
On this roundtable episode of IT Visionaries, we explore the impact A.I. and technology are having on society and cybersecurity with Casey Ellis, the founder and CTO of Bugcrowd and Malcolm Harkins, a cybersecurity advisor, coach and board member.
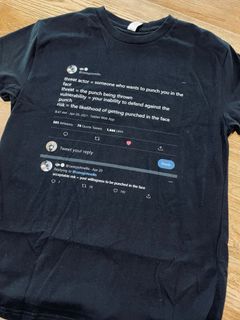
The Bar Fight Risk Taxonomy
After hearing "vulnerability" and "threat" used interchangeably for a >9,000th time I decided to do something about it, and the Bar Fight Risk Taxonomy was born.
On Project Zero's 90+30 vulnerability disclosure policy changes
Google is acknowledging the increasing prevalence of n-day exploitation in the wild, particularly over the past 18 months (e.g. the CISA/NSA memo) have taken their next step in refining how they strike balance between these forces.
Security Research and Disclosure: The Unauthorized Biography — Nullcon March 2021
Title: Security Research and Disclosure: The Unauthorized Biography | Casey John Ellis | Nullcon Conference March 2021
A thought re vulnerability research clustering
The fact that insecure software pipelines are exploitable feels a little like the idea that bugs exist in old F/OSS code, or that a chip design might not be 100% perfect. It's almost QED - but in the defensive realm, people weren't looking there.
Help! My Social Media has been hacked!
I know you do security stuff with computers and my Twitter/Facebook/Instagram/etc has been hacked! It's posting all kinds of strange stuff that isn't from me. What do I do to stop this???
Van Buren v. United States — Oral Argument
The Supreme Court heard oral argument in Van Buren v. United States, a case concerning a statute of the Computer Fraud and Abuse Act (CFAA) and violations of terms of service agreements.