

tag
#security
The technical heart: vulnerability research, disclosure, threat analysis, the craft of finding and fixing
AI and bug bounties: notes from 68 minutes on Across the Pondcast
68 minutes with Tib3rius and Andy Swift on Across the Pondcast, cut down to the salient points and timestamped: how Bugcrowd started, what AI has actually done to bug bounty, why a VDP is the sane fallback, and where researchers should point next.
A lot of people are just sitting on zero-day right now
I sat down with Ashish Rajan on the AI Security Podcast after Black Hat. The bit worth writing down: the triage queues are noisy enough that good researchers are sitting on zero-day. Plus export controls, attack graphs, port 3000, and why leaders should go use this stuff at home.
Hacker Summer Camp and notes from 63 minutes on the "slopalcious" slopdemic
63 minutes with Aaron Mog on Zero Sum, cut down to the salient points and timestamped: the slopdemic, the two axes, why the vulnpocalypse hasn't happened yet, and who is still hiring juniors.

Non-Cooperative Defense and Impermissive Access
wp2shell handed the quiet policy debate about non-cooperative defense its first civilian-scale live-fire exercise.

Wake Me After the Vulnpocalypse
AI industrialized the discovery of vulnerabilities, not the exploitation of them, and that distinction is the whole argument. What we have is a slopdemic. The fragility was always there, and the real exposure is the gap between instant discovery and human-speed remediation.
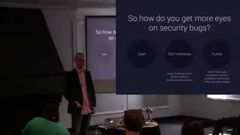
The Amended Linus's Law
Marcus Hutchins says LLMs just killed "many eyes make all bugs shallow." He's half-right. Linus's Law was never wrong, it was incomplete: the missing variable is incentive, and AI just gave it teeth on both sides.
Slopdemic, Not Vulnpocalypse (Yet)
I joined Sherrod DeGrippo on the Microsoft Threat Intelligence Podcast this week to talk about how AI is reshaping vulnerability research, disclosure, and patching.
AI Didn't Break Vulnerability Disclosure. It Exposed What Was Already Broken.
There's a sentence I keep coming back to from a conversation Josh Bressers and I had recently on Open Source Security: we&
The Hitchhiker's Guide to Bug Bounty and Vulnerability Disclosure in 2026
Post-Mythos vulnerability disclosure: a 2026 field guide for vendors and researchers on AI-era bug bounties, slop triage, and rebuilding ecosystem norms.
Auditing My 2026 Security Predictions: Five Months In
Back in December I made eight predictions for what 2026 would bring in security. We're four months in, so it's
Thoughts on the #slopdemic
Move over #vulnpocalypse — there's a new term we need to talk about: the #slopdemic. AI didn't invent low-quality vuln reports, but it just turbocharged them, and F/OSS is drowning.
The "irrational asymmetry" in threat behavior
We've traditionally thought about defense through the lens of a financially motivated attacker or a nation state — predictable rewards. Open it to