

A lot of people are just sitting on zero-day right now
 Casey Ellis · · 4 min read
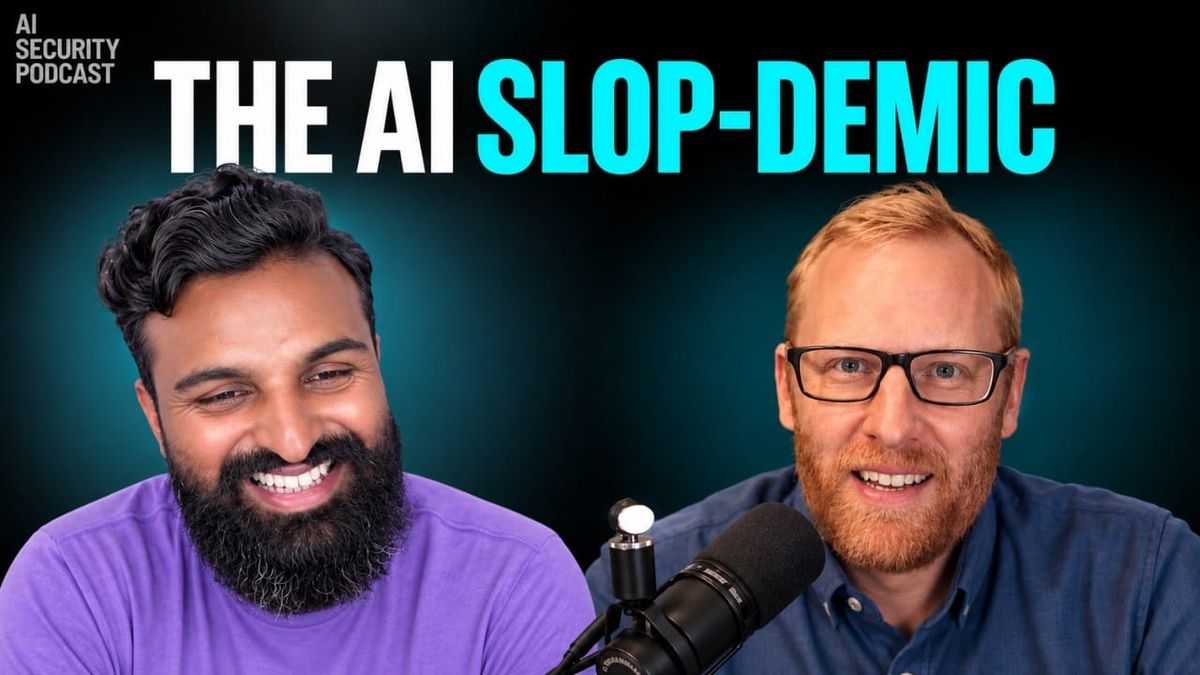
I sat down with Ashish Rajan on the AI Security Podcast a couple of weeks after Black Hat.
The episode was pitched as "what did you see at RSA and Black Hat this year," and we did that, but the bit that stuck with me afterwards (and the bit Ashish put in the title, so clearly it stuck with him too) was something I said almost in passing about the state of the triage queue:
A lot of people are just sitting on zero day now.
I've written about the slopdemic enough times that I'm not going to redo the definition here. If you're new to the term, Wake Me After the Vulnpocalypse is the long version. The short version is that AI collapsed the cost of finding and reporting bugs at the same time, and every intake queue on the internet is now paying for it.
What I hadn't really said out loud until this conversation is the second-order effect of that.
If you're on the outside trying to help, whether that's through a bounty program, a VDP, or just emailing a vendor because you found something nasty, it's actually pretty hard to get anyone to listen right now. The queues are noisy enough that a lot of the folks with genuinely good stuff have looked at the effort involved in getting it triaged and gone "nah." They're not thinking about breaking bad. They're not selling it.
It's just too hard, so they're sort of sitting on it.
That is a much weirder risk than "too many reports." The reports you're drowning in are, by definition, the ones you can see. The zero-day that never got submitted because the researcher couldn't be bothered fighting your queue is invisible until someone else finds it.
Nature finds a way, and all that.
Ashish asked the obvious follow-up, which was whether the volume is real or whether it's all slop, and the honest answer is that it's both. The cost of getting from "huh, that's interesting" to "here's a working chain" has dropped, especially for competent operators. The "you must be this tall to ride" bar has dropped too, so there are more people jumping in, and a lot of them are, to use my own numbers from the show, a three out of ten for usefulness and an eleven out of ten for enthusiasm. That's not new. The community has always done community things and you've always had to figure out what to do with that. What's new is that the good stuff and the noise got the same discount at the same time.
A few other things from the conversation that I'd defend in print:
You're not going to export-control your way to a safer internet. I happened to be in DC the week the export control stuff landed, and my read on it is that a big part of the reaction was policymakers suddenly realizing this was possible in the first place. It's been possible for three or four years. People have been tearing apart firmware with open-weight models and unrestrained frontier models for that long, it's just that everyone started talking about it at once. If there's one thing fifteen years of bug bounty and vulnerability disclosure has taught me, it's that telling the internet "no, don't do that please" does not work. The internet isn't listening.
Attackers and exploits don't function as a list. They function as a graph with a starting point and an impact endpoint, and traversing it is still very much down to the skill and the context of the operator. That's the part of the vulnpocalypse that hasn't arrived yet. Point-and-pwn is real and trivial issues will absolutely fall out of it, but that space is also contested now: it's so easy to find that stuff that you'll dupe out as a bounty hunter or bump into a competing adversary as an actual bad guy. The people I'm actually worried about are the true VR folks, who haven't delegated their intelligence to the model, they've picked up a loyal wingman and gone 10 to 100x. (Ashish was glad I didn't say co-pilot. Same.)
Port 3000 at Black Hat was pretty wild. I'm close with the folks who run the NOC at Black Hat and DEF CON, and two things they saw this year are worth sitting with. One, they saw zero-day across the wire, which doesn't normally happen at that con because anyone with the tradecraft knows it'll get caught. That shifted because there are now people with the capability and not the tradecraft. Two, a bunch of vibe-coded apps bound to every interface, and people sitting around waiting for exactly that to happen. Bob from accounting building himself a tool because his boss told him to use more AI is, in isolation, a good thing. Bob shipping the prospect list in cleartext on port 3000 is the part nobody wrote a policy for.
If you lead a security org, go use this stuff at home. A lot of the senior folks I talk to aren't aware of what AI can do defensively, or from a build standpoint, because corporate policy has been "don't use it." People are going to use it anyway. Relying on policy to stop them is not great defensive thinking, and if leadership doesn't know the art of the possible you end up with a massive gap between the folks running the business and what the workforce is actually doing, which is an internal threat problem with a bow on it. The fix is boring: get a harness, play with it, automate something dumb around the house, poke at your own home network. You don't have to be technical, the stuff is literally designed for people who aren't. If you still think AI is stupid because it miscounted the Rs in strawberry three years ago, you're doing it wrong at this point.
Deception tech is about to have a good time. It was always a good solution. It's now an obviously good solution, because everyone just noticed they don't know what their agents are doing. Shout out to the folks who've been quietly grinding on it for twelve or thirteen years while the rest of us were busy shifting left.
There's more in there (the defender's dilemma, why "bug bounty is dead" makes me roll my eyes, Ashish's very good point about the token cost of the $10,000 bug heading toward $100 and my very predictable reply about what an attacker would pay for it), but that's the stuff I keep coming back to.
Full episode above, chapters in the description if you want to skip to a bit. Thanks for having me on, Ashish.
Comments ·
members only