

Casey Ellis
Find it and fix it
A fun exercise: run various models against deliberately vulnerable apps, and eval them on their ability to identify the vulns and effectively patch them
Prompt-injection bumper stickers
Prompt injection is climbing out of the chat box and into the physical world. Print an adversarial instruction big enough for a camera to
Words mean things
If the AI era teaches you anything, let it be the lesson that words mean things.
Slopdemic, Not Vulnpocalypse (Yet)
I joined Sherrod DeGrippo on the Microsoft Threat Intelligence Podcast this week to talk about how AI is reshaping vulnerability research, disclosure, and patching.
My Clanker Setup
A mate messaged me this week asking whether I'd ever written up my clanker setup: which harness I run, which models, what
AI Didn't Break Vulnerability Disclosure. It Exposed What Was Already Broken.
There's a sentence I keep coming back to from a conversation Josh Bressers and I had recently on Open Source Security: we&
The Hitchhiker's Guide to Bug Bounty and Vulnerability Disclosure in 2026
Post-Mythos vulnerability disclosure: a 2026 field guide for vendors and researchers on AI-era bug bounties, slop triage, and rebuilding ecosystem norms.
Coordinated, Until It Isn't
Everyone has a take on Moksha's 89-vuln XAPI drop. Almost everyone misses the same thing: it wasn't one decision, it was four: go public, go Day-0, withhold patches from Citrix, lean into the "shittrix" frame. Coordinated disclosure runs on goodwill, and the goodwill runs out sometimes.
Auditing My 2026 Security Predictions: Five Months In
Back in December I made eight predictions for what 2026 would bring in security. We're four months in, so it's
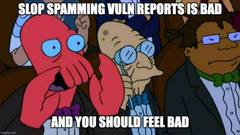
Thoughts on the #slopdemic
Move over #vulnpocalypse — there's a new term we need to talk about: the #slopdemic. AI didn't invent low-quality vuln reports, but it just turbocharged them, and F/OSS is drowning.
The "irrational asymmetry" in threat behavior
We've traditionally thought about defense through the lens of a financially motivated attacker or a nation state — predictable rewards. Open it to
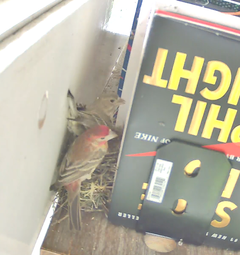
Continued Monitoring of the Situation
Week two of an AI-powered House Finch nest monitor: four model biases, a Wyze cam back from the dead, and a full pipeline rewrite before the eggs hatch.